About Me
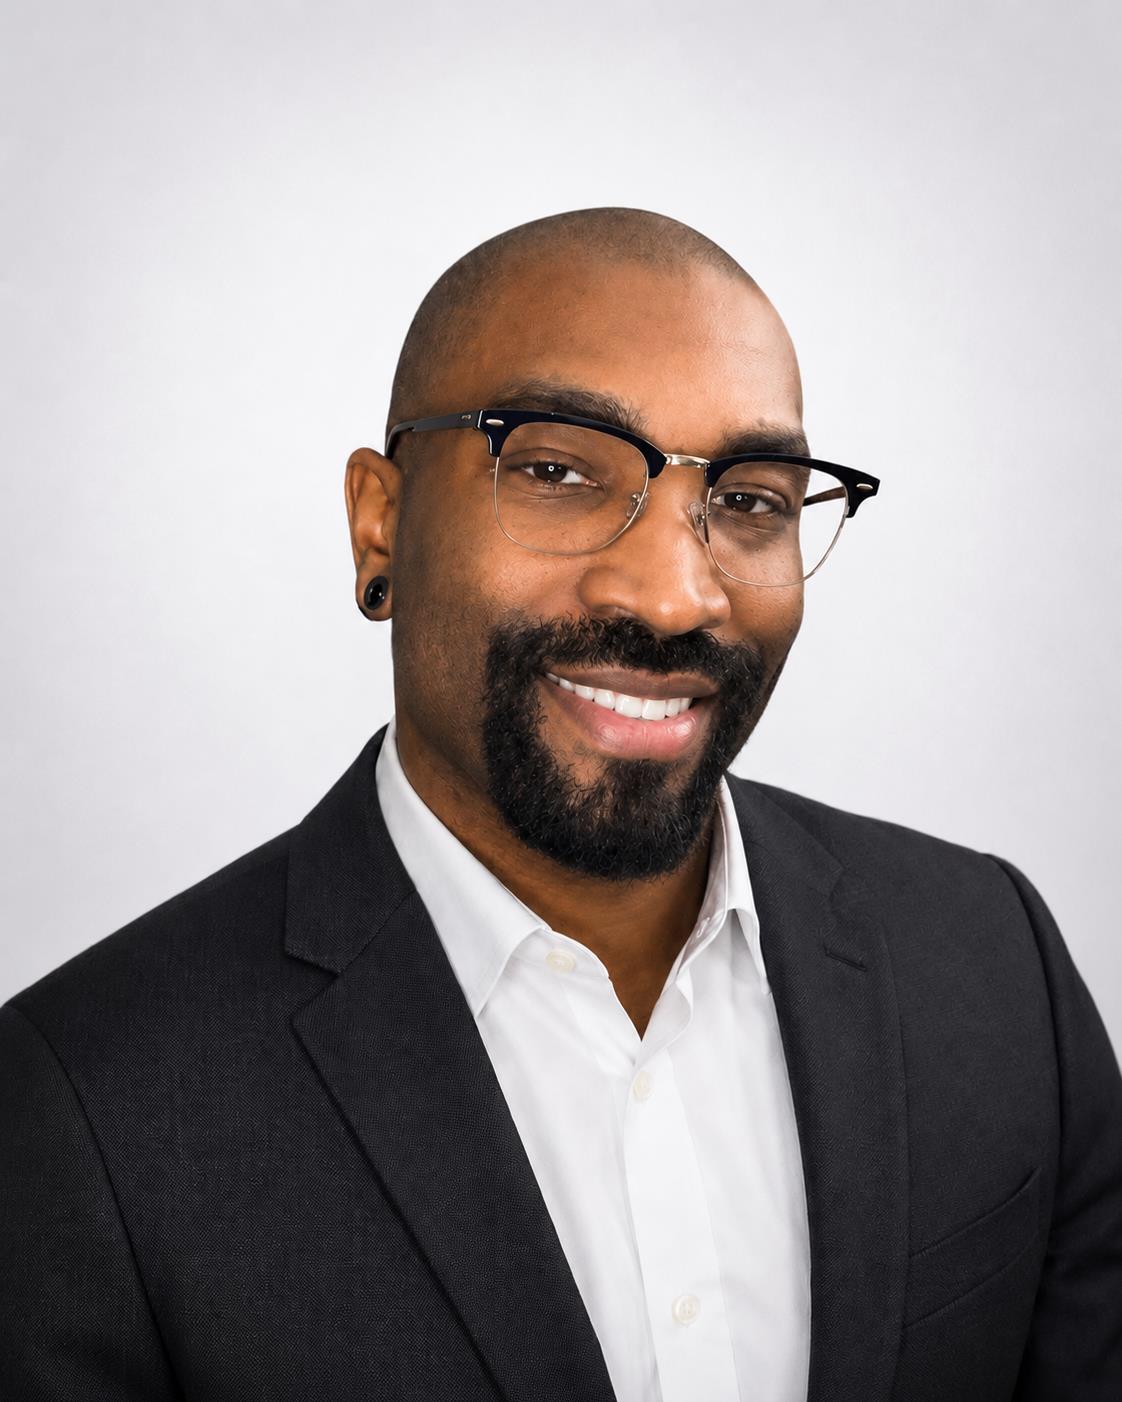
Kyrell Green
Graduation: December 2026
I’m always learning — reading tech TL;DRs, tinkering with devices and systems, and figuring out what makes things tick.
Cybersecurity Growth
SOC & SIEM/XDR
Deploying and validating a Wazuh SIEM/XDR lab for endpoint telemetry, alert triage, and incident response — and layering an AI-agentic workflow on top for alert classification and escalation.
Network Security
Designing a routed, two-subnet lab with pfSense firewalling, ACLs, and segmentation, and mapping traffic against the OSI/TCP-IP models to reason about trust boundaries.
Threat, Vulnerability & Risk
Running Nmap-based asset discovery and vulnerability assessments, analyzing malware and phishing samples, mapping findings to MITRE ATT&CK, and documenting risk and incident-response steps.
Career Direction
Preferred role(s): Cyber Security Analyst, IT Helpdesk
Work environment: Hybrid/Remote
Ideal job description: Security SOC Analyst
Team: Like-minded people who are passionate about not just what they do, but why they do it.
Future goals: I hope to make a positive impact doing work I genuinely enjoy.